
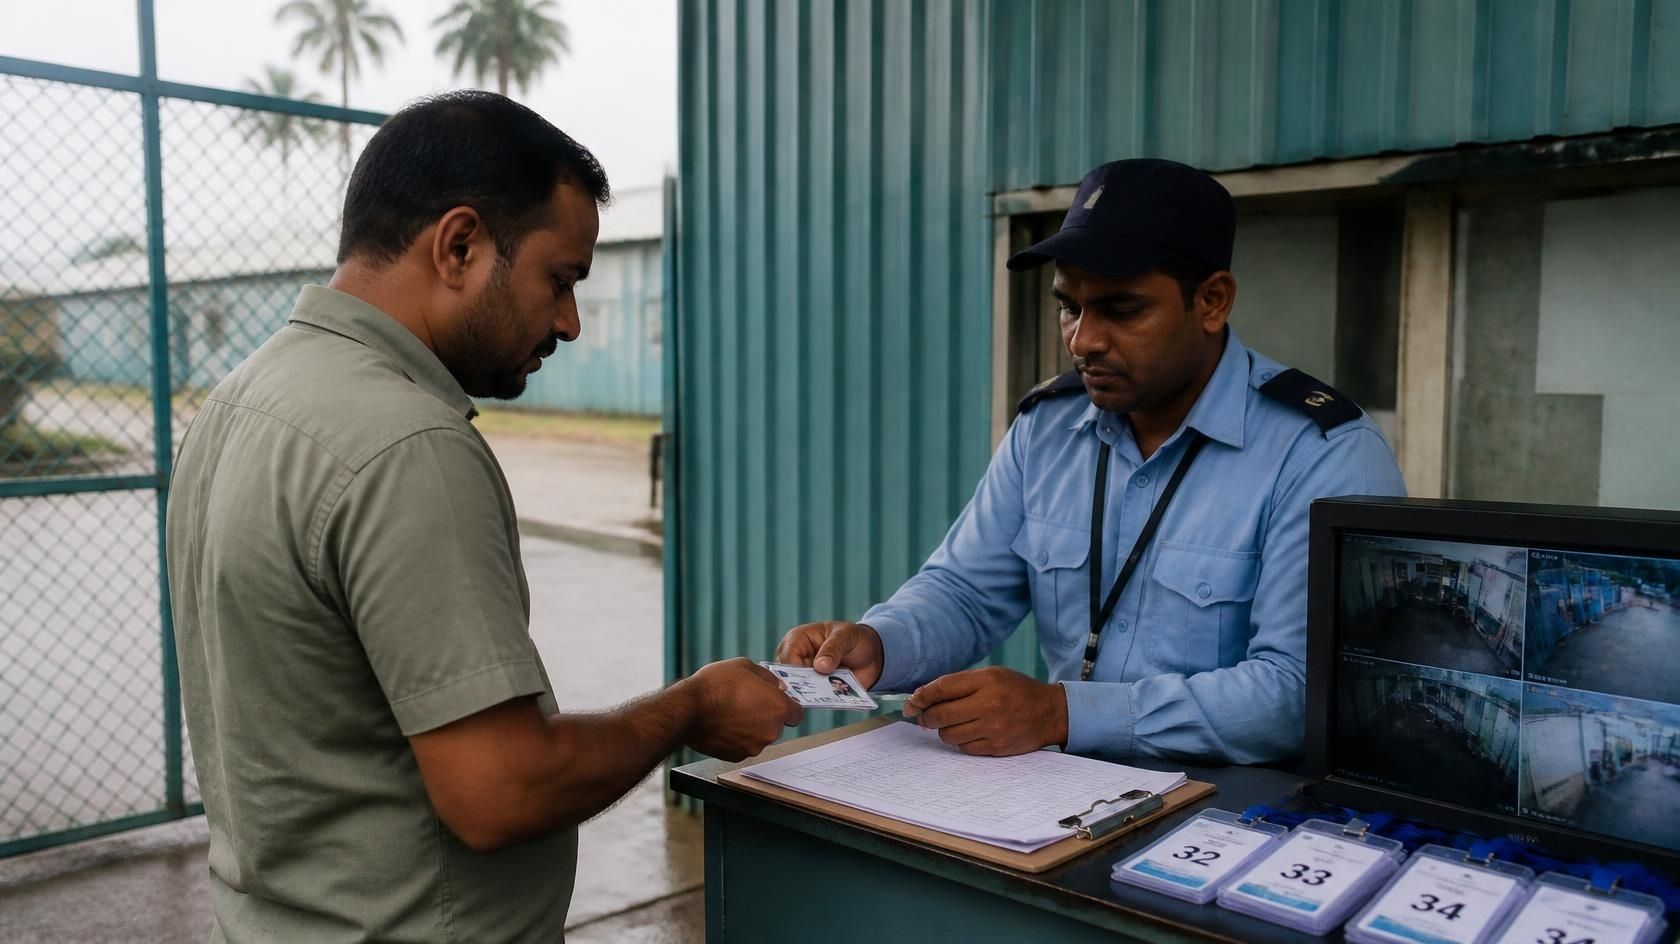
A buyer's compliance auditor walks up to your reception desk unannounced. She asks for the visitor log from three Tuesdays ago. The guard flips through a spiral notebook, finds the page, and it's missing the sign-out time for four names. She asks who those four people were. Nobody remembers.
That five-minute exchange can cost a factory its social-compliance rating, and with it, an order.
Access control and visitor management gets treated as a guard-and-gate problem when it is actually a documentation problem wearing a security uniform. The gate stops the wrong person from walking in. The paperwork is what proves to a buyer, six months later, that the gate did its job on every single day, not just the day of the visit.
Most factories building this from scratch buy turnstiles and biometric readers first and think about the audit trail last. That order is backwards, and it is expensive to fix once badges are already in circulation and the layout is fixed.
This article gives you the zoning logic, the visitor workflow, and the container-security detail an export-factory audit actually checks, in the order you should build them, not the order vendors sell them.
Why Generic Security Advice Fails an Export Factory
A badge system and a turnstile satisfy a facilities manager. They do not satisfy a buyer's audit, because the audit is not asking "can unauthorised people get in." It is asking "can you prove, with a paper or digital trail, who was where and when, for the last twelve months."
The compliance angle changes what you design for. A domestic factory can get away with a guard's memory. An export factory selling to a brand with a C-TPAT-aligned or WRAP-style supply chain security programme cannot: the evidence itself is the deliverable, not just the physical control.
How Do You Zone a Factory for Access Control?
Zoning is the first decision, and it drives everything after: badge colours, escort rules, camera placement. A factory with four zones and clear rules for each will out-perform a factory with expensive hardware and no zoning logic.
Zone | Who Enters Freely | Access Control Measure | Typical Audit Focus |
|---|---|---|---|
Public / Reception | Visitors, vendors, couriers | Reception desk, sign-in, badge issuance | Visitor log completeness |
General Factory Floor | All badged employees | Employee ID card, turnstile or supervised entry | Tailgating, shared badges |
High-Security Areas (finished goods store, sample room, label store) | Named, listed staff only | Card-restricted door, CCTV, entry/exit log | Access list currency, camera coverage |
Restricted Areas (server room, HR/document room, chemical store, seal storage) | Single named custodian plus backup | Dual control or keyed access, logged every entry | Custodian list, log against roster |
A factory that cannot produce a current, signed access list for its high-security and restricted zones fails this section regardless of how good the hardware is. Auditors check the list against actual badge logs, not against what the policy document says should happen. The restricted-area list (chemical store, seal storage) is also exactly where a proper hazard identification and risk assessment earns its keep, since who is allowed near a hazard and who is actually trained to be near it are two different questions.
Field note: At a woven-bottoms factory in Chattogram, the finished goods store had a card reader logging every entry, but the access list handed to the auditor had 11 names, while the reader log for the prior month showed 19 unique card IDs entering. Eight employees had been added to the physical access group during a rush period and never removed. That single discrepancy triggered a full walk-through of every restricted zone.
Building-Envelope and Perimeter Basics
Zoning inside the building assumes the perimeter already holds. A continuous boundary fence, controlled gates, adequate perimeter lighting, and clear sight lines with no stacked material against the fence line are the baseline layer underneath everything else, the same clear-sight-line logic that drives fire load calculation and compartmentation, where stacked material against a wall is as much a fire-spread problem as a security blind spot. Ground-floor windows in secure areas should be secured, and roof access should be locked and logged: it is a common gap because nobody thinks of it as a "door."
What Does a Buyer-Audit-Ready Visitor Workflow Look Like?
The workflow has to survive two conflicting pressures: guards under pressure to move a queue of vendors quickly, and auditors expecting zero gaps in the record. A five-step process handles both if every step produces a record.
Pre-registration by the host department. The employee expecting the visitor submits the name, company, purpose, and expected zones at least a day ahead where possible. This is what lets a guard verify identity rather than just accept a name.
Photo ID verification at arrival. Match the ID to the pre-registration, not just to a name on a list. Walk-ins without pre-registration get verified against the host department by phone before entry, not waved through.
Badge issuance, zone-coded. A visibly distinct badge, different colour or shape from employee ID, printed with the zones the visitor is cleared for and, if the layout allows it, an escort requirement stated on the badge itself.
Escort for any zone above general reception. Anyone entering the factory floor, and anyone entering a high-security or restricted zone under any circumstances, moves with a named escort. The escort's name goes in the log, not just the visitor's.
Sign-out and badge return. Time out, badge collected, and (this is the step that gets skipped under time pressure) a check that the sign-out time is actually filled in before the guard moves to the next visitor.
Visitor-Log-Fields Checklist
A log missing any of these fields is an audit finding waiting to happen. Build the log, paper or digital, around this list, not around whatever a stationery shop happened to stock.
Visitor full name (as on photo ID)
ID type and number
Company / organisation represented
Host name and department
Purpose of visit
Time in and time out
Badge number issued
Zones authorised
Escort name (if applicable)
Guard/receptionist initials
Retain visitor logs for at least twelve months, and check your specific buyer's requirement, since some ask for longer. A log that exists but was thrown out after three months reads to an auditor exactly like a log that never existed.
Container and Cargo Area Security: Where Export Factories Get Extra Scrutiny
Export factories carry a security obligation domestic manufacturers do not: the finished-goods supply chain from packing to port is a documented target for tampering and smuggling concerns, and buyer audits weight this section heavily.
Container inspection before loading is not optional and not a glance through the door. A seven-point inspection, checking the front wall, left side, right side, floor, ceiling/roof, inside/outside doors, and outside/undercarriage, should be completed and signed for every container, with the signed checklist retained alongside the shipping documents.
Seal control is where programmes most often break down under audit. High-security bolt seals should be stored in a locked cabinet with restricted, named access; logged by seal number at issuance and again at application to the container; and matched against the shipping document seal number before the container leaves the yard.
A missing or duplicate seal number in the log is treated by most buyer audits as a critical finding, not a minor one, because it directly maps to the cargo-tampering risk the whole framework exists to manage. Keep the cargo yard itself inside your zoning table too: it is a high-security area, not an extension of the general factory floor, and any chemicals stored nearby for container fumigation or treatment belong in a properly segregated area under a chemical storage segregation and compatibility plan, not a side shelf in the yard office.
The Access Control Findings That Fail Factories Most Often
The same handful of findings recur across social-compliance and supply-chain-security audits, and every one of them is a process failure, not a hardware failure.
Finding | Why It Happens |
|---|---|
Shared badges | One card assigned to a shift or a role instead of a named individual makes the entry log meaningless: it proves a badge entered, not a person |
Unrecorded visitors | Someone entering through a side door, or a "quick five-minute" vendor visit that never reaches the log book |
Tailgating at turnstiles | A second person following a badge holder through without swiping, the single most common finding on walk-throughs, because it requires no malicious intent, only politeness |
Ex-employee badges not deactivated | Card access is cancelled in payroll but never pulled from the physical access control system, leaving an active credential with no owner |
Run a card-audit against your current HR roster monthly, not annually. This single habit closes the ex-employee badge gap before it becomes a finding, and it takes one person about twenty minutes for a mid-sized factory, the same fixed-interval discipline that separates a preventive maintenance program from a predictive one, where waiting for a failure to force the check is always the more expensive route.
Field note: A knitwear exporter running a quarterly self-audit against their buyer's own checklist found 14 active badges belonging to people who had resigned in the prior six months, none flagged in HR's exit process because badge deactivation sat with a different department and nobody owned the handoff. Moving badge deactivation into the exit-interview checklist itself, signed off before the final pay is released, closed the gap in one cycle.
Evidence an Auditor Will Actually Ask to See
Beyond the visitor log and access lists, a buyer or C-TPAT-aligned audit typically pulls documentation across these areas. Have each of these ready before the auditor arrives, not assembled the night before.
Requirement | Evidence to Produce |
|---|---|
Security procedure | Signed written policy with a distribution/acknowledgement record |
Employee screening | Pre-employment identity verification records |
Visitor control | Complete logs, cross-checked against badge-issuance records |
Access lists | Current, signed lists for every high-security and restricted zone |
Container inspection | Seven-point checklist, signed per shipment |
Seal control | Numbered issuance log matched to shipping documents |
CCTV | Written coverage plan and stated retention period |
Incident response | Investigation records and corrective actions taken |
Training | Attendance records with a defined refresh cycle |
Building the Habit: A Quarterly Self-Audit
Factories that pass buyer audits consistently, rather than scrambling before each one, run their own internal review every quarter using the buyer's own checklist as the template. It surfaces the badge-and-roster mismatches, the missing seal numbers, and the stale access lists while there is still time to fix them quietly.
This is the difference between a security programme and a security event that happens once a year when the auditor's visit is confirmed.
Final Word
Access control hardware buys you very little on its own. What passes an audit, and what actually stops a bad outcome, is the discipline of a complete, current, cross-checked record: who is on a badge list, who signed a visitor in and out, and which seal number went on which container. Build the paperwork habit before you build the gate.
Discussion0
Loading the discussion…